Navigation

Get in touch
Logo
News

Utimaco HSM: Keys in certified hardware

Utimaco builds hardware security modules in Aachen and ships three lines: general purpose applications, payments and key management. We pick the right series with you, integrate it into your applications and guide the move to post-quantum algorithms.

Try product
  • FIPS 140-3 Level 3
  • Common Criteria EN 419 221-5
  • eIDAS QSCD
  • VS-NfD
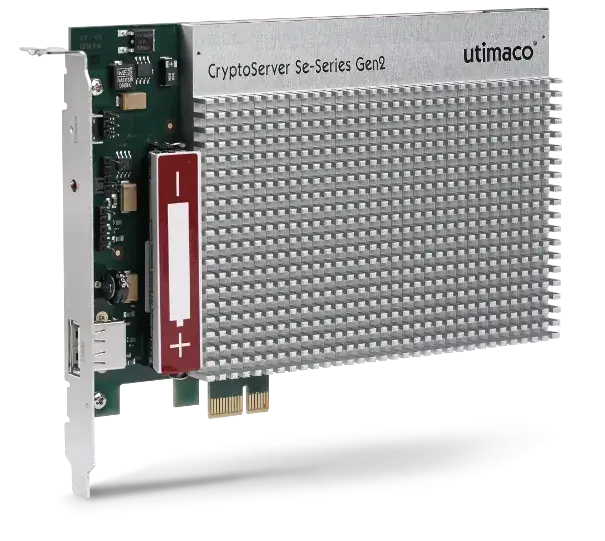
Utimaco u.trust General Purpose HSM of the Se-Series as a PCIe card
Product photo: Utimaco

Utimaco at a glance

A hardware security module generates and stores cryptographic keys inside a certified device. The key never leaves that boundary in plaintext, and the application calls signing and decryption through the PKCS#11, CNG or CXI interface. Utimaco covers general purpose applications, payments and key management with a single platform.

Cryptography and hardware security modules are our core competence. We know the Utimaco firmware, the container separation and the migration paths between CryptoServer and u.trust. As a Trust as a Service partner, reseller, EMEA distributor and training partner we deliver technology, licenses and knowledge from one source.

General Purpose, Payment, Key Management
FIPS 140-3 Level 3, CMVP 5223
ML-KEM, ML-DSA, LMS, HSS, XMSS
Appliance, PCIe card, as a Service

OTOKO® and Utimaco

At Utimaco our role reaches well beyond reselling, and we rank among the largest partners of the vendor worldwide. Four roles sit under one roof, from delivery as a service to the training of your staff.

Trust as a Service partner

We deliver Utimaco modules as a service, with operations, monitoring and a documented key ceremony.

Value added reseller

Devices and licenses come with sizing, integration and support, not as a plain delivery.

Value added distributor EMEA

For u.trust LAN Crypt and DiskEncrypt we supply and support partners across Europe, the Middle East and Africa.

Exclusive training partner

Utimaco training runs through us worldwide and exclusively, from administration to key management.

The series in detail

u.trust General Purpose HSM Se-Series

The Se-Series is the current line for general purpose applications and the successor to the CryptoServer Se models. It separates up to 31 tenants in their own containers and takes a field upgrade to post-quantum algorithms.

View device illustration
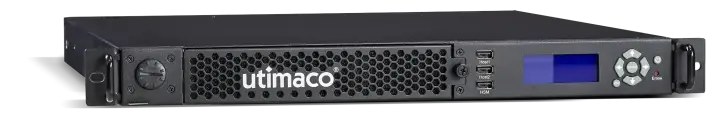
Utimaco u.trust General Purpose HSM as a rack appliance
Rack applianceProduct photo: Utimaco

Models

u.trust General Purpose HSM Se-Series: Models
Se100101 RSA-2048 operations per second
Se2k2,050 RSA-2048 operations per second
Se5k5,100 operations, with 8, 16 or 31 containers
Se15k15,000 RSA-2048 operations per second
Se40k40,000 operations, with 8, 16 or 31 containers
Form factors
LAN appliance, PCIe card
Operation
Your own data center, General Purpose HSM as a Service, Connection to AWS, Azure and Google Cloud

Certifications

  • FIPS 140-3 Level 3, CMVP 5223
  • FIPS 140-2 Level 3
  • Common Criteria
  • PCI PTS HSM v3

Features

  • Up to 31 separated containers, each with its own PKCS#11 partitions
  • Quantum Protect delivers ML-KEM, ML-DSA, LMS, HSS and XMSS
  • Further packages for 5G, blockchain and Double Key Encryption
  • Free simulator for tests before procurement
  • Custom firmware through the CryptoServer SDK
Vendor information

u.trust General Purpose HSM CSe-Series

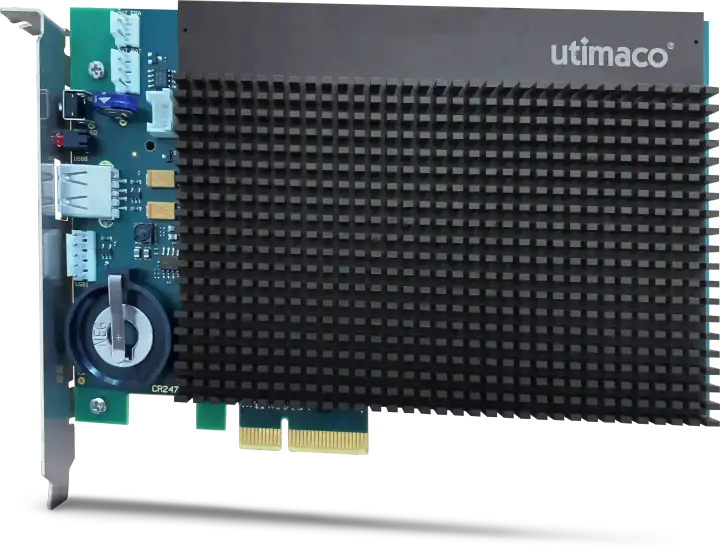
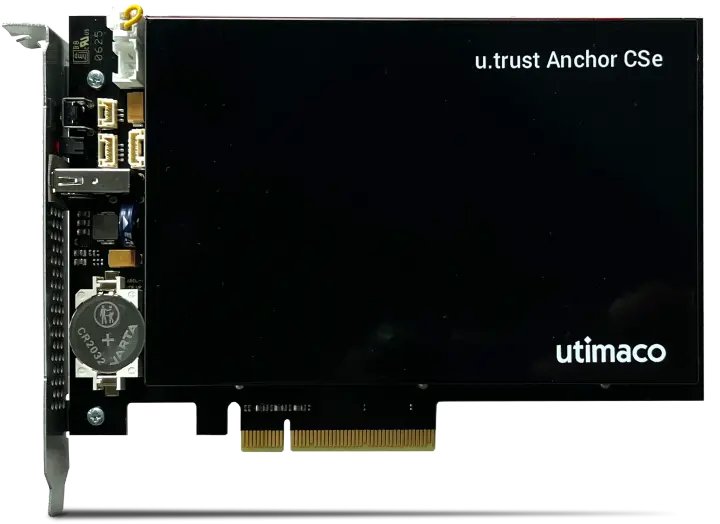
The CSe-Series adds the highest physical protection tier to the Se line and was introduced in October 2025. A tamper-active sensor film erases the keys as soon as someone opens the housing.

View device illustration
Utimaco u.trust General Purpose HSM of the CSe-Series as a PCIe card
PCIe cardProduct photo: Utimaco

Models

u.trust General Purpose HSM CSe-Series: Models
CSe100101 RSA-2048 signatures per second, one container
CSe2k2,050 signatures per second, four containers
CSe5k5,100 signatures, with 8, 16 or 31 containers
Form factors
LAN appliance, PCIe card
Operation
Your own data center, Hosting at a service provider

Certifications

  • FIPS 140-3 Level 4 in progress
  • PCI PTS HSM v3

Features

  • Tamper-active sensor film with immediate key erasure
  • Up to 25,000 ECC signatures per second
  • Same post-quantum algorithms as the Se-Series
  • Simulator and application packages for eIDAS configurations

Vendor information

CryptoServer General Purpose HSM

The CryptoServer carries the approvals that the public sector and trust services ask for today. Among them are Common Criteria per EN 419 221-5, eIDAS QSCD and VS-NfD. For new projects we plan the move to the u.trust Se-Series from the start.

View device illustration
Utimaco CryptoServer General Purpose HSM as a PCIe card
PCIe cardProduct photo: Utimaco

Models

CryptoServer General Purpose HSM: Models
Se12Entry level for small signing loads
Se52Medium load in PKI environments
Se500High load for trust services
Se1500Highest load of the CryptoServer line
Form factors
LAN appliance V5, PCIe card
Operation
Your own data center, Trust as a Service
Lifecycle
End of life in March 2027, the successor is the u.trust General Purpose HSM Se-Series

Certifications

  • FIPS 140-2 Level 3
  • Common Criteria EAL4+ per EN 419 221-5
  • eIDAS QSCD
  • VS-NfD, EU RESTRICTED, NATO RESTRICTED

Features

  • Application package CC eIDAS for remote signing per EN 419 241-2
  • Application package VS-NfD for classified environments
  • PKCS#11, CNG and CXI interfaces
  • Simulator for test and development
  • Also available through Trust as a Service

Vendor information

Atalla AT1000 Payment HSM

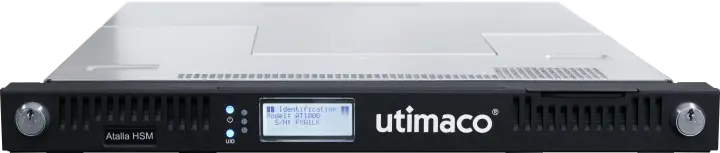
The AT1000 protects PINs, card data and keys in payment traffic. It passes the audits that card networks and regulators require for payment hardware. Issuers, acquirers and payment service providers run it in their own data center or as a service.

Utimaco Atalla AT1000 payment HSM as a rack appliance
Rack applianceProduct photo: Utimaco

Models

Atalla AT1000 Payment HSM: Models
AT1000Up to 10,000 transactions per second
AT1000 partitionsSeparate keys and administrators per partition
Form factors
LAN appliance
Operation
Your own data center, Payment HSM as a Service

Certifications

  • FIPS 140-3 Level 3
  • FIPS 140-2 Level 4 physical
  • PCI PTS HSM v3
  • PCI PIN and PCI DSS

Features

  • Remote management for master keys, key injection and firmware
  • Partitioning for several tenants on one device
  • Free simulator for integration tests
  • Also available as Payment HSM as a Service

Vendor information

Enterprise Secure Key Manager

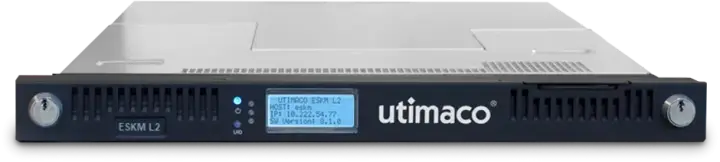
The Enterprise Secure Key Manager administers keys for databases, storage and applications over the KMIP protocol. It takes the administration work off the HSM. It scales from a virtual instance up to an appliance with a built in hardware security module.

Utimaco Enterprise Secure Key Manager as a rack appliance
Rack applianceProduct photo: Utimaco

Models

Enterprise Secure Key Manager: Models
ESKM L1Virtual instance, FIPS 140-2 Level 1
ESKM L21U appliance for regular operations
ESKM L31U appliance with a built in General Purpose HSM
ESKM L4Highest expansion stage of the line
Form factors
Virtual instance, 1U appliance
Operation
Your own data center, Virtualization, as a Service

Certifications

  • Common Criteria EAL2+
  • FIPS 140-2 Level 1 for L1
  • FIPS 140-3 Level 2 in progress

Features

  • KMIP 1.0 to 2.1 for third party systems
  • More than two million keys per cluster
  • Support for post-quantum algorithms
  • Also available as Enterprise Key Manager as a Service

Vendor information

How you find the right series

Four questions decide the choice: the required validation level, the load in signatures per second, the interfaces of your applications and the operating model. We clear them in a workshop and record the result in a decision paper.

Validation level

FIPS 140-3 Level 3 covers the regular case. Level 4 demands an active sensor film and shows up at public bodies and operators of critical infrastructure. For trust services Common Criteria per EN 419 221-5 counts instead of FIPS.

Load and tenants

The models differ by a factor of 400 in RSA operations per second. The Se100 delivers 101 operations, the Se40k delivers 40,000. Whoever separates several applications picks a model with 8, 16 or 31 containers.

Interfaces

Your applications speak PKCS#11, CNG or CXI, while key management systems speak the KMIP protocol. We check in the simulator up front whether your database, PKI or signing service works with the chosen firmware.

Operating model

You can run the devices yourself, have us run them for you or use Utimaco Trust as a Service. The entire solution runs in German data centers.

What we deliver around Utimaco

We do not only supply the device, we supply the whole chain before and after it: selection, integration, key ceremony, monitoring and operations. One team accompanies you from consulting to operations.

  • HSM consulting and integration

    We size the series, set up containers and partitions and connect PKCS#11 and CNG to your applications. We document the key ceremony in an audit proof form.

    HSM & Key Management

  • PQC readiness

    We record which keys and protocols rest on RSA and ECC, because quantum computers threaten both algorithms. We then plan the move to ML-KEM and ML-DSA with the Quantum Protect firmware.

    Post-Quantum Cryptography

  • Cybersecurity

    We monitor the devices in operation, separate administration from application and review roles and logs on a regular schedule. We feed the events into your SIEM, the system that collects and rates security messages.

    Cybersecurity

Standards and evidence

These five rules decide the selection and the documentation on Utimaco projects. We tell you which series carries each one today and which proof is still in progress.

Requirement / Demands / OTOKO® delivers
RequirementDemandsOTOKO® delivers
FIPS 140-3Validated crypto modules with a defined physical protection levelSe-Series at Level 3 with CMVP number 5223, CSe-Series at Level 4 in progress
Common Criteria EN 419 221-5Certified signing module for trust servicesCryptoServer with EAL4+ and the CC eIDAS application package
PCI PTS HSMCertified hardware for PINs and card keysAtalla AT1000 per v3, plus PCI PIN and PCI DSS
eIDASQualified signature creation device at the trust service providerCryptoServer as QSCD, remote signing per EN 419 241-2
BSI VS-NfDClearance for classified data up to VS-NfDCryptoServer with the VS-NfD package, also EU and NATO RESTRICTED

Frequently asked questions about Utimaco

Related topics

You would like to learn more about

Utimaco

Utimaco builds hardware security modules in Aachen and ships three lines: general purpose applications, payments and key management. We pick the right series with you, integrate it into your applications and guide the move to post-quantum algorithms.

Our clients

Our Partners

  • Microsoft
  • Microsoft Azure
  • Amazon AWS
  • Google Cloud
  • Thales Group
  • Arrow ECS
  • Vodafone
  • IBM
  • Veeam
  • Atlassian
  • JetBrains
  • NinjaOne
  • OPSWAT
  • Utimaco
  • Eviden

Accessibility

Adjust the display to suit your needs.

A simple version is not available for this page yet.

Settings currently apply to this visit. Allow saving in Cookie settings to remember them.