Navigation

Get in touch
Logo
News

Entrust nShield: Security World across all devices

Entrust builds the nShield family around a shared key management architecture called Security World, so appliance, PCIe card and service carry the same keys. We select the devices with you, replace older XC models and connect the interfaces to your applications.

Try product
  • FIPS 140-3 Level 3
  • Common Criteria EAL4+
  • eIDAS QSCD
  • BSI AIS 20/31
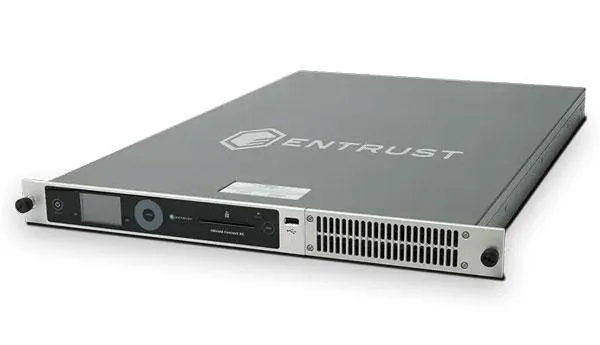
Entrust nShield 5c as a network appliance
Product photo: Entrust

nShield at a glance

A hardware security module creates and stores keys in certified hardware and never releases them in plaintext. At Entrust all current nShield devices share the Security World architecture and the same interfaces PKCS#11, OpenSSL, JCE, CAPI and CNG, nCore and Web Services, so you can mix models in one estate.

Cryptography and hardware security modules are our core competence. We know how a Security World is built, how the XC models are replaced and how CodeSafe runs custom code inside the device, and we run your project from the first selection through the key ceremony into operations.

nShield 5c, 5s, as a Service, Edge, Issuance
FIPS 140-3 Level 3, CMVP 4745
ML-DSA, ML-KEM, SLH-DSA, LMS
Appliance, PCIe card, USB device, as a Service

The series in detail

nShield 5c

The nShield 5c is the network appliance of the current generation and replaces the nShield Connect XC. It carries FIPS 140-3 Level 3 and Common Criteria EAL4+ per EN 419 221-5 and serves PKI, code signing, databases and mobile networks.

View device illustration

Models

nShield 5c: Models
BaseThree client licenses included, up to 10 possible
MidUp to 20 client licenses
HighUp to 1,000 client licenses, 11,680 RSA-2048 operations per second
nShield 5c 10GFour SFP+ ports
Form factors
1U network appliance
Operation
Your own data center, Hosting at a service provider

Certifications

  • FIPS 140-3 Level 3, certificate 4745
  • The CMVP lists certificate 4745 under nShield 5s
  • Common Criteria EAL4+ with AVA_VAN.5 and ALC_FLR.2 per EN 419 221-5
  • Basis for QSCD per EN 419 241-2
  • Random numbers per BSI AIS 20/31

Features

  • Firmware 13.8.3 on the High model with 23,890 ECDSA P-256 operations per second
  • ML-DSA-44 with 3,130 signatures per second
  • Two power supplies, hot swappable
  • Separated roles for provider and tenant
  • Remote management through nShield Remote Administration and KeySafe 5
  • CodeSafe 5 runs custom code in containers inside the device
Vendor information

nShield 5s

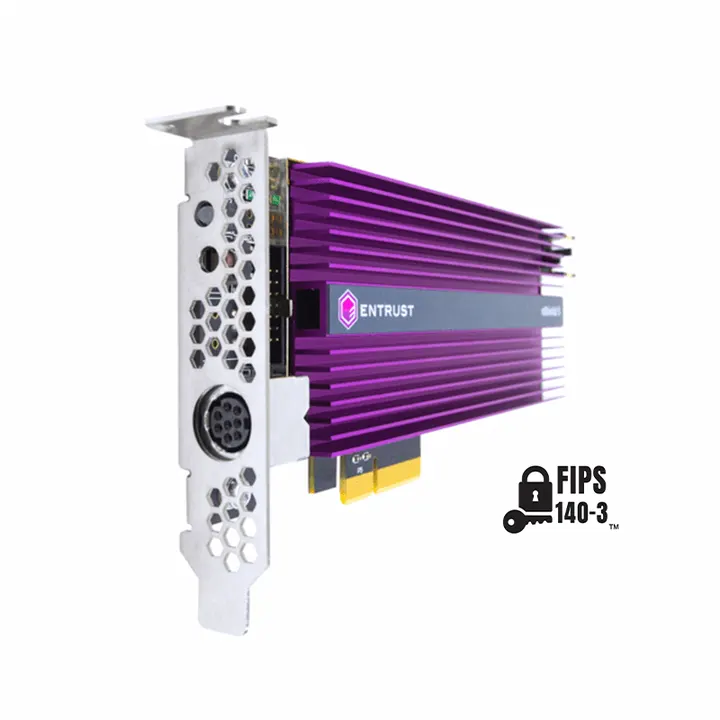
The nShield 5s is the PCIe card of the same generation, replaces the nShield Solo XC and delivers 13,614 RSA-2048 operations per second on the High model. The Multi-Tenancy option puts separated Security Worlds on a single card.

Entrust nShield 5s as a PCIe card
Product photo: Entrust

Models

nShield 5s: Models
BaseSmallest of the three performance tiers
MidMiddle performance tier
High13,614 RSA-2048 and 21,826 ECDSA P-256 operations per second
Multi-Tenancy for nShield 5sSeparated Security Worlds on one card
Form factors
Low profile PCIe 2.0 x4 card
Operation
Application server, Your own data center

Certifications

  • FIPS 140-3 Level 3, CMVP certificate 4745
  • Validated on July 31, 2024, valid until July 30, 2029
  • Common Criteria EAL4+ per EN 419 221-5
  • eIDAS QSCD

Features

  • Card with 25 watts of power draw
  • External smart card reader included
  • ML-DSA-44 with 2,780 signatures per second
  • Same post-quantum algorithms as the nShield 5c
  • Successor of the nShield Solo XC

Vendor information

nShield as a Service

With nShield as a Service Entrust runs the devices in its own data centers, among them one in Germany, and you keep the keys and the Security World. You choose between four performance tiers and between self managed and fully managed operations.

Data center for Entrust nShield as a Service
Product photo: Entrust

Models

nShield as a Service: Models
Basic400 RSA-2048 signatures per second
Standard800 RSA-2048 signatures per second
Premium6,000 RSA-2048 signatures per second
Enterprise16,000 RSA-2048 signatures per second
Form factors
Hosted service
Operation
Data centers run by Entrust, Disaster recovery in the cloud

Certifications

  • The US region is certified to PCI DSS

Features

  • Data centers in Germany, the United Kingdom, the United States and Australia
  • Operations either self managed or fully managed
  • CodeSafe is supported
  • Option for disaster recovery in the cloud
  • Keys and Security World stay with the customer

Vendor information

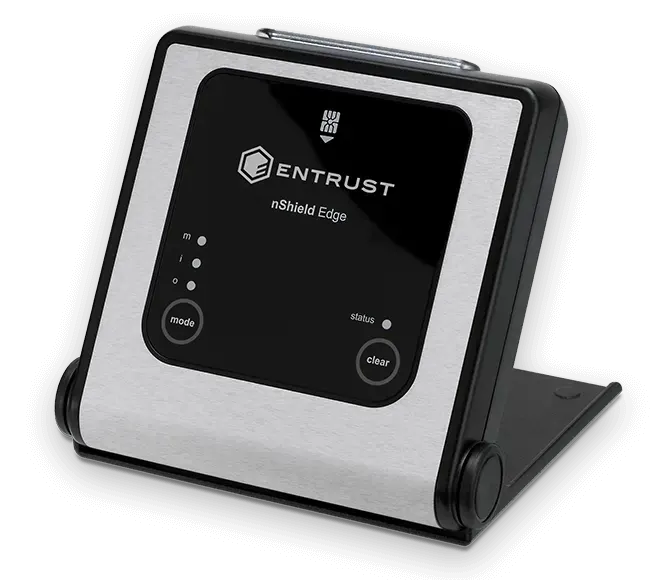
nShield Edge

The nShield Edge is a portable USB device with a smart card reader for the offline root of a PKI, for development and for your own keys in the cloud. The datasheet dates from 2020 and names neither FIPS 140-3 nor post-quantum algorithms.

Entrust nShield Edge as a USB device
Product photo: Entrust

Models

nShield Edge: Models
nShield Edge FIPS 140-2 Level 2Variant at validation level 2
nShield Edge FIPS 140-2 Level 3Variant at validation level 3
Developer EditionEdition for development and test
Form factors
USB device
Operation
Workplace, Development environment

Certifications

  • FIPS 140-2 Level 2
  • FIPS 140-2 Level 3
  • No statement on FIPS 140-3

Features

  • About 2 RSA-2048 operations per second
  • Smart card reader for administration
  • For offline root certificate authorities, development and your own keys in the cloud
  • All figures come from the datasheet of 2020

Vendor information

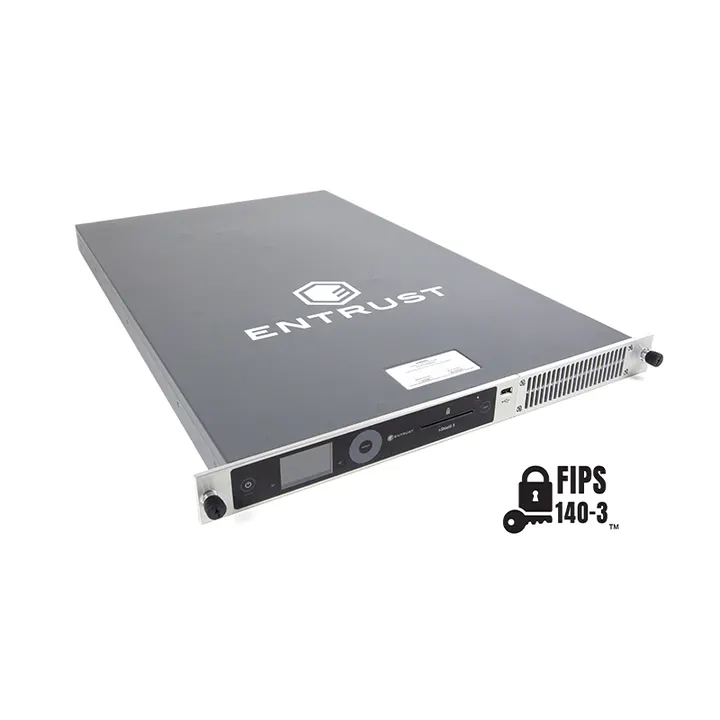
nShield Issuance HSM

The nShield Issuance HSM prepares EMV data and generates keys for issuing cards, and EMV is the standard for chip cards. It works only with Entrust Adaptive Issuance and the Key Manager from version 6.6 and is not a general payment HSM per PCI PTS.

Entrust nShield Issuance HSM
Product photo: Entrust

Models

nShield Issuance HSM: Models
nShield HSMi1U appliance for card issuance
Variant FIPS 140-2 Level 2Edition at validation level 2
Variant FIPS 140-2 Level 3Edition at validation level 3
Form factors
1U appliance
Operation
Your own data center

Certifications

  • FIPS 140-2 Level 2
  • FIPS 140-2 Level 3
  • No payment HSM approval per PCI PTS

Features

  • Preparation of EMV data for card issuance
  • Generation of the keys for cards
  • Usable only with Entrust Adaptive Issuance
  • Key Manager from version 6.6 required

Vendor information

nShield XC

The XC line with nShield Connect XC and Solo XC is no longer sold but stays in mainstream maintenance until the end of 2027. The Connect XC carries FIPS 140-2 Level 2 and 3 as well as Common Criteria EAL4+ and delivers 3,500 or 8,600 RSA-2048 operations per second on the Mid and High tiers.

Models

nShield XC: Models
nShield Connect XC Mid3,500 RSA-2048 operations per second
nShield Connect XC High8,600 RSA-2048 operations per second
nShield Solo XCPCIe card, the successor is the nShield 5s
Form factors
1U network appliance, PCIe card
Operation
Your own data center, Application server
Lifecycle
End of sale on October 31, 2025, mainstream maintenance until December 31, 2027, the successors are nShield 5c and nShield 5s

Certifications

  • FIPS 140-2 Level 2 and Level 3
  • Common Criteria EAL4+

Features

  • Excluded from the end of sale are the -CC, -NTS, TSOP and Issuance variants
  • The Connect CLX image is no longer updated after Security World 13.3
  • The successors are the nShield 5c and the nShield 5s

Vendor information

How you pick the right model

Four points decide the choice at Entrust: the required validation level, the load with the number of tenants, the need for custom code and the operating model. We work through the points with your team and record the decision.

Validation level and approvals

nShield 5c and 5s carry FIPS 140-3 Level 3 and Common Criteria EAL4+ per EN 419 221-5 and serve as the basis for QSCD. The nShield Edge and the Issuance HSM stay at FIPS 140-2, which rarely satisfies tenders that demand proof.

Load and tenants

The nShield 5c delivers 11,680 RSA-2048 operations per second on the High model, and the nShield 5s card reaches 13,614. As a service the tiers range from 400 to 16,000 signatures per second, and the Multi-Tenancy option delivers separated Security Worlds.

Custom code and interfaces

All current devices speak PKCS#11, OpenSSL, JCE, CAPI and CNG, nCore and Web Services. Whoever needs custom logic inside the device uses CodeSafe 5 and runs the code in a container within the security boundary.

Operating model

You can run the devices yourself, you can hand operations to us, or you can book nShield as a Service with data centers in Germany. The entire solution runs in German data centers.

Our work around nShield

The Security World needs planning, documentation and care, and integration, monitoring and the move from XC to the 5 series come on top. One team accompanies you from consulting to operations.

  • HSM consulting and integration

    We plan the Security World, set up cards and appliances and connect your applications through PKCS#11, JCE and CNG. We plan the replacement of the XC devices along your maintenance dates.

    HSM & Key Management

  • PQC readiness

    We record which applications rest on RSA and ECC, because quantum computers can break both, and we plan the move to ML-DSA and ML-KEM. Firmware 13.8.0 of August 22, 2025 brings these algorithms, and the CMVP revalidation is still running.

    Post-Quantum Cryptography

  • Cybersecurity

    We monitor the devices, separate the roles of provider and tenant, review the Security World cards and report events into your SIEM. The SIEM collects and rates security messages.

    Cybersecurity

Standards and evidence

Five rules decide the selection and the documentation on Entrust projects. We name the device that carries each rule and state open validations separately.

Requirement / Demands / OTOKO® delivers
RequirementDemandsOTOKO® delivers
FIPS 140-3Validated crypto modules with a defined physical protection levelnShield 5s at Level 3 with certificate 4745, valid until July 30, 2029, the nShield 5c cites the same certificate
Common Criteria EN 419 221-5Certified signing module for trust servicesnShield 5c and 5s with EAL4+, AVA_VAN.5 and ALC_FLR.2, certified through NSCIB
eIDAS EN 419 241-2Qualified signature creation device for remote signingnShield 5c and 5s as the basis for QSCD per EN 419 241-2
BSI AIS 20/31Certified random number generatorRandom number generator of the nShield 5c per AIS 20/31
PCI DSSCertified operating environment for card datanShield as a Service is certified to PCI DSS in the US region

Frequently asked questions about Entrust

Related topics

You would like to learn more about

Entrust

Entrust builds the nShield family around a shared key management architecture called Security World, so appliance, PCIe card and service carry the same keys. We select the devices with you, replace older XC models and connect the interfaces to your applications.


Our clients

Our Partners

  • Microsoft
  • Microsoft Azure
  • Amazon AWS
  • Google Cloud
  • Thales Group
  • Arrow ECS
  • Vodafone
  • IBM
  • Veeam
  • Atlassian
  • JetBrains
  • NinjaOne
  • OPSWAT
  • Utimaco
  • Eviden

Accessibility

Adjust the display to suit your needs.

A simple version is not available for this page yet.

Settings currently apply to this visit. Allow saving in Cookie settings to remember them.