Encryption
File & folder encryption
File encryption for small businesses, midsize companies and enterprises: plan, roll out and operate LAN Crypt. Standard use and VS-NfD are considered separately.
Learn about this service ®
Cybersecurity with OTOKO®
We encrypt files and storage media, secure incoming files with OPSWAT MetaDefender and test your software, cloud infrastructure and AI applications for exploitable vulnerabilities. From basic protection in a small company to projects subject to VS-NfD and NATO RESTRICTED requirements.
Find the right protectionAnalysis · Integration · verifiable results
OTOKO® × OPSWAT / Cologne 2026

As an OPSWAT partner in Germany, we combine product selection and technical implementation with direct dialogue. In 2026, we held the OPSWAT Bootcamp in Cologne. The film offers insights into the joint work, conversations and on-site training.
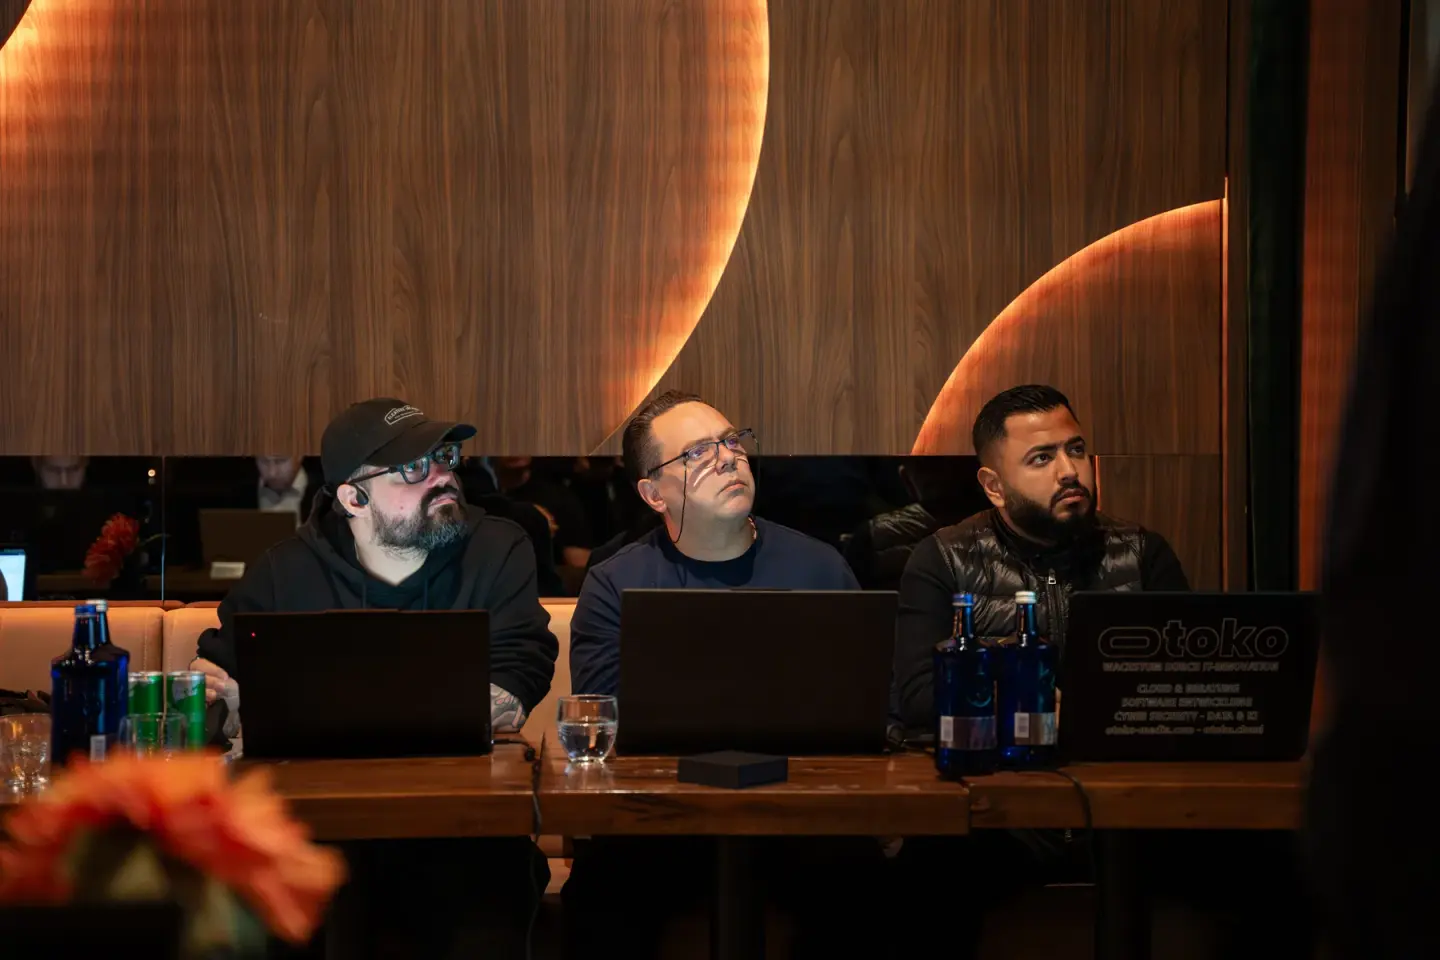
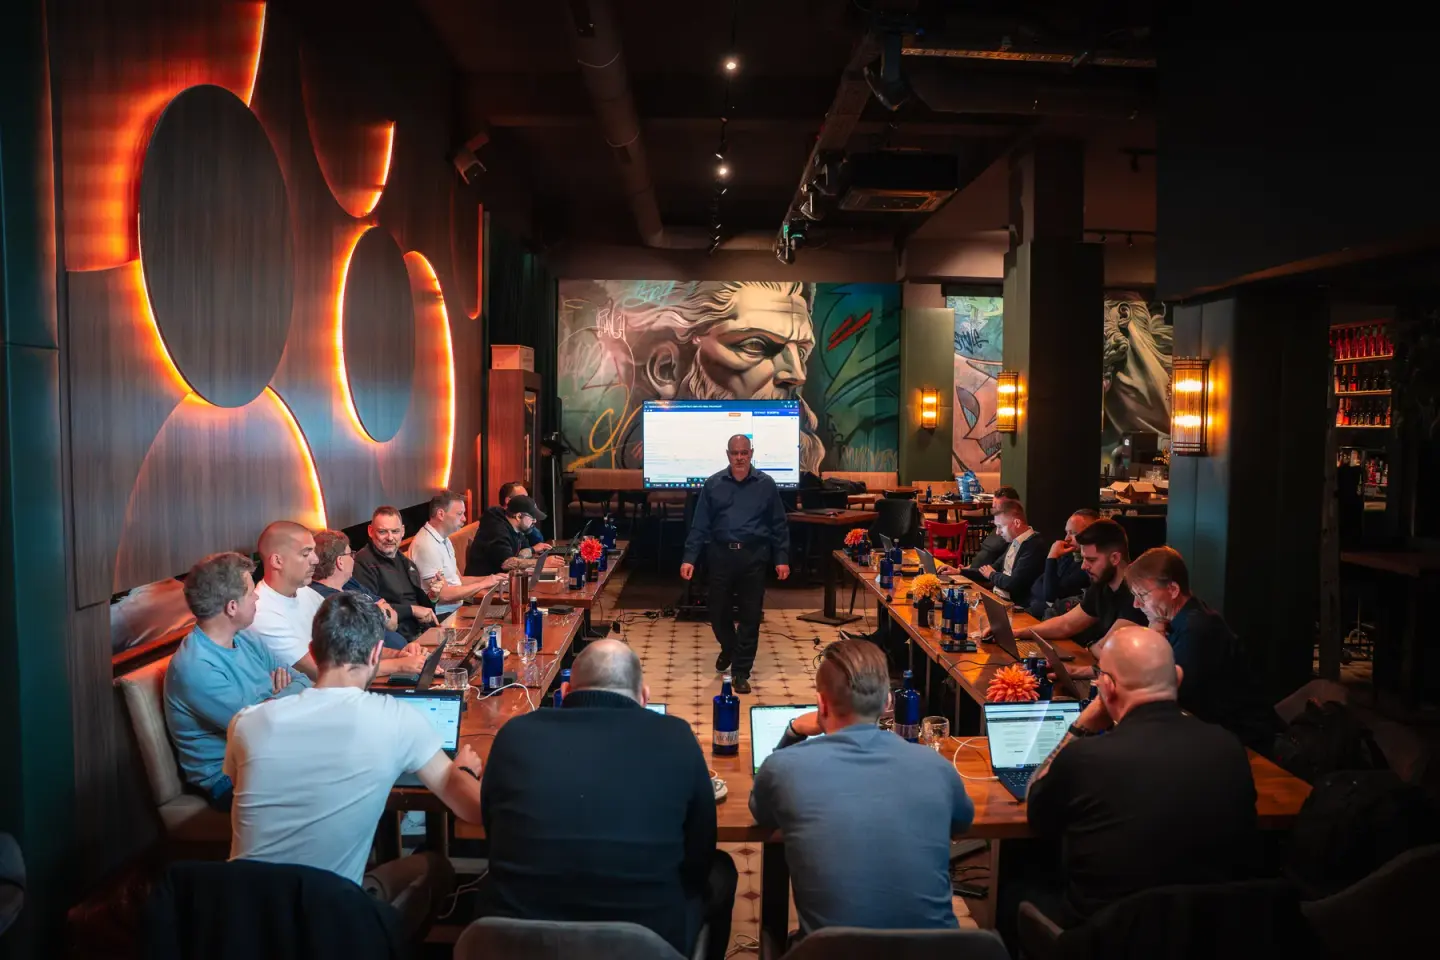
In the film: impressions from the training room, conversations with participants and the handing out of participant materials. The photos show our team and the joint session in Cologne.
Learn about OPSWAT file security with OTOKO®Know-how in software analysis: understanding root causes and making technical findings usable for development teams.
The worldwide OTOKO® team combines software development, infrastructure and the implementation of demanding IT projects.
Determines architecture, test scope and the required evidence, from everyday business to especially sensitive projects.
Nine topics. Concrete tasks.
A lost hard drive, a manipulated job application and access to other customers’ data need different answers. Choose the area where your risk arises. On each topic page, you will find our scope of services, planning questions and a concrete project scenario.
Encryption
File encryption for small businesses, midsize companies and enterprises: plan, roll out and operate LAN Crypt. Standard use and VS-NfD are considered separately.
Learn about this serviceEncryption
DiskEncrypt for corporate devices: procurement, rollout, recovery and support. From small businesses to enterprises, with a separate edition for VS-NfD.
Learn about this serviceEncryption
Encrypted USB drives, SSDs and hard drives from small businesses to enterprises. Standard storage media and Kobra VS for special protection requirements.
Learn about this serviceFile security
Integrate OPSWAT MetaDefender Core: multiscanning, CDR, file type detection, DLP and SBOM for uploads, downloads and controlled file transfers.
Learn about this serviceOffensive security
Authorized pentests for SaaS, APIs, PaaS applications and legacy software: business logic, tenant separation, evidence and remediation with OTOKO®.
Learn about this serviceOffensive security
OTOKO® tests networks, cloud configuration and IaaS with authorization: access paths, identities, segmentation, prioritized findings and retesting.
Learn about this serviceOffensive security
OTOKO® analyzes AI applications: data access, prompt injection, RAG, agent permissions and secure tool calls. With 15 years of software analysis experience.
Learn about this serviceSensitive environments
Plan encryption projects for VS-NfD and NATO RESTRICTED: review product approval, operations and personnel requirements (including Ü3) separately.
Learn about this serviceOffensive security
Agree on the result, define a fixed fee: if the agreed evidence is not produced in the authorized penetration test, the success-based fee does not apply.
Learn about this serviceUtimaco / OTOKO®

Exclusive EMEA distributor for DiskEncrypt and u.trust LAN Crypt. Your partner for custom adaptations, installation, commissioning, maintenance and Level 1-3 support.
File and folder encryption
Protect confidential files in a targeted way and control access through a planned role and key model. OTOKO® supplies u.trust LAN Crypt and integrates the solution into your file storage, workflows and administration.
For small businesses, midsize companies and enterprises: standard deployment and separate editions for classified information. We align licensing, user scope and support with your organization.
This entry names VS-NfD. No EU or NATO approval is shown here for this version.
Disk encryption
Protect stored data on company devices against unauthorized reading. OTOKO® supplies DiskEncrypt and handles the integration of authentication, key management, device rollout and recovery.
For small businesses, midsize companies and enterprises: standard deployment and separate editions for classified information. We align licensing, user scope and support with your organization.
These details apply to the versions named and their respective deployment and operating conditions. Customer-specific modifications and changes are reviewed for their effect on the scope of approval before implementation. BSI list of approved products.
Kobra Infosec GmbH / External storage media
In addition to encrypted standard storage media, we offer this product family for particularly sensitive areas of use. It can also be used for regular confidential business data; use with classified information additionally requires the matching approval and mode of operation.
OTOKO® is a partner and distributor for MENA, APAC and the European Economic Area (EEA). We offer favorable project terms for your procurement, matched to quantity, configuration and deployment region.
External encrypted storage device
For mobile provision and handover of larger data volumes. We align the required model and capacity with your procurement needs and plan how the medium is issued, transported and returned.
Encrypted USB-C flash drive
For compact, portable storage media in clearly defined workflows. Authorized users, intended target systems and handling in case of loss are part of the selection, along with the appropriate storage capacity.
Matched to your daily work
Sensitive documents are often spread across laptops, file servers and shared folders at the same time. We help you organize these data paths and build protection that your team can operate. This includes permissions, a defined process for lost devices and a tested recovery. Security measures are implemented in prioritized steps, so that day-to-day business and support capacity are taken into account.
A SaaS product must separate customer data, control uploads and deliver new features safely. We look at the application, APIs, platform services and operational access together. AI features add data sources, model responses and tool permissions. Findings are prepared so that product owners understand their significance and developers can fix the root cause in a targeted way.
Here, a good technical product alone is not enough. Information category, valid approval, approved configuration, operating processes and access authorization must fit together. We plan the technical implementation in line with these requirements. Requirements for Ü1, Ü2 or Ü3 as well as permitted communication channels are clarified with the responsible officers before sensitive information or system access is transferred.
Pentesting / Result as a Service
Do you want to know whether a specific attack on your application or infrastructure is actually possible? We agree in advance which security problem is to be proven within the approved scope. If the agreed proof is not achieved, you do not pay the success-based penetration test fee.
So that the model is unambiguous for both sides, we define testing rights, preconditions, quality of proof and acceptance in writing. Not every finding automatically counts as the agreed result. On the detail page, we show how a security question becomes a clearly defined agreement on the result.
The fee model in detail
From individual modules to end-to-end protection
A customer portal accepts a file. Before an employee opens it, it is checked and, if necessary, sanitized. In internal storage, roles and encryption provide access protection. On the mobile device, storage media encryption is added. An application test, in turn, checks whether another customer could retrieve the file through a manipulated request.
We align these transitions with each other: who is allowed to decrypt? Where is scanning done? What happens if there is an error? Which evidence is retained? This creates a transparent process with clear responsibilities.
Guidance for your project
First, we determine which information, applications and business processes need to be protected. From this we derive a manageable sequence, for example clarifying access and recovery, encrypting mobile devices and securing public file uploads. A penetration test is scheduled where its results enable concrete decisions. You receive a clearly scoped starting point with responsibilities and documented work results.
The two cover different situations. Disk encryption protects stored data on a powered-off or correctly locked storage medium within the scope of the respective solution. File encryption can enforce permissions across storage locations and transfer paths. Whether both make sense depends on device operation, collaboration, data paths and protection needs. An already logged-in, authorized user remains a separate security case.
We align the scope with the use case: from a modest corporate network to a project with classified information. For VS-NfD or NATO RESTRICTED, specific products, versions, conditions of use and the operating concept are reviewed. If an assignment requires security-cleared personnel, the required evidence and access must be clarified in advance on a project basis. Ü3 denotes a security clearance for people, not a level of encryption.
Before the start, we agree on a fixed amount and a specific, reproducibly provable security finding within a permitted test scope. If this agreed proof is not provided, the agreed success-based penetration test fee does not apply. The result criteria, preconditions and acceptance are set out in writing. Remediation, additional consulting or retests are charged only if ordered separately. A test without a matching finding is not a guarantee of complete security.
This is clarified before the architecture decision. Depending on the edition, MetaDefender can also be operated in your own environment. Data transfer, external analysis, telemetry and update paths must match the respective data class. An on-premises scanner alone does not yet make a transition between classified networks permissible. We therefore take into account the complete approval process and the responsible bodies.
An actionable finding describes preconditions, affected functions, reproduction steps, technical impact and a classification within the business process. We discuss with your team where the root cause should be fixed. If agreed, a retest verifies the specific correction. For AI applications, we additionally consider model variability, data sources and the permissions of connected tools.
File encryption for small businesses, midsize companies and enterprises: plan, roll out and operate LAN Crypt. Standard use and VS-NfD are considered separately.
We determine protection needs, the number of users and the operational requirements. You receive a suitable selection for regular business use or a separately reviewed, approved edition. Product, version and included services are specified in detail in the quote.
Which documents belong together, who needs to read them and how do project members change? Together, we translate these workflows into protection domains and policies. Existing file shares and applications are factored in, so that encryption follows your actual work processes.
Keys require designated owners and a process for joiners, leavers, deputies and emergencies. Administration and business-side data access are deliberately kept separate. A recovery concept is agreed with the authorized parties and tested in practice.
A pilot tests opening, editing, saving and the intended exchange of files. Business applications, synchronization and backup are examined for how well they work together with the selected solution. The rollout follows only after these results have been evaluated.
We plan deployment of the version approved under BSI-VSA-10966 based on your data pathways and protection domains. Installation, configuration and customer-specific adaptations are assessed against the approved deployment conditions. The agreed commissioning and handover into maintenance and support follow afterward.
Personnel files, development documents, quotes and customer data already deserve protection in normal business operations. Your company does not need to handle government contracts or process classified information for this. Together, we determine which files are encrypted, who needs access on the business side and how deputies can be arranged. The standard solution is aligned with these workflows; an approved edition is added when your specific protection needs require it.
A small business can start with a protected storage area for management and HR. In midsize companies, for example, separate project teams, multiple sites and external collaboration come into play. For enterprise structures, we additionally plan delegated administration, systematic permission changes and clearly assigned key responsibilities. The selection takes into account client versions, existing storage locations, application compatibility and how authorized people continue working even after a device change.
A file share first governs who may access data through a specific access path. File and folder encryption adds to this protection: access to the content additionally depends on the keys required. What matters is which data pathways the chosen solution actually covers. Together, we look at local storage, shared directories, copy operations and exchange with partners. This shows where confidential content is processed and where different or additional protection is needed. The application perspective remains important here. Authorized people still need to be able to edit files; at that moment, plaintext can exist. Encryption therefore does not automatically prevent data loss through an already authorized or compromised user. Endpoint protection, sensible roles and secure exchange procedures remain part of the overall setup. In the pilot, we examine the intended workflows and document their limits. This gives your team a clear statement of what is protected and what responsibility remains elsewhere.
The next step
Describe your current situation and the desired outcome. For a classified project, an unclassified task description is sufficient at first. We then jointly clarify the appropriate exchange channel and the required preconditions.












